80% of small businesses have experienced IT-related downtime. Managed IT means ongoing oversight and support for a business’s technology, rather than calling for help only after something breaks. When comparing managed IT service provider reviews, look beyond star ratings to see whether providers cover security, backups, incident response, compliance, and day-to-day support.
It’s reasonable to expect a managed IT service provider to do more than keep devices running. Your systems also need protection, a workable recovery plan, and support that adapts as your business changes. This guide explains what managed IT includes and how to compare providers on the capabilities that matter to your operations.
Use this practical checklist to assess security coverage, backup and recovery, incident response, compliance support, scalability, and long-term service. It can help you distinguish ongoing, accountable support from a narrow list of technical tasks and decide what kind of partnership fits your business.
Key Takeaways
- Compare providers by the protection and recovery work they perform, not just by the tools they list.
- Look for a clear incident-response process that explains how issues are prioritized, communicated, and resolved.
- Match compliance support to your organization’s obligations and the frameworks relevant to your operations.
- Assess whether a provider can adapt its support as your systems, staff, and business needs change.
- Use a consistent checklist to compare service scope, security capabilities, and long-term support before choosing a partner.
1. Cybersecurity and backup coverage
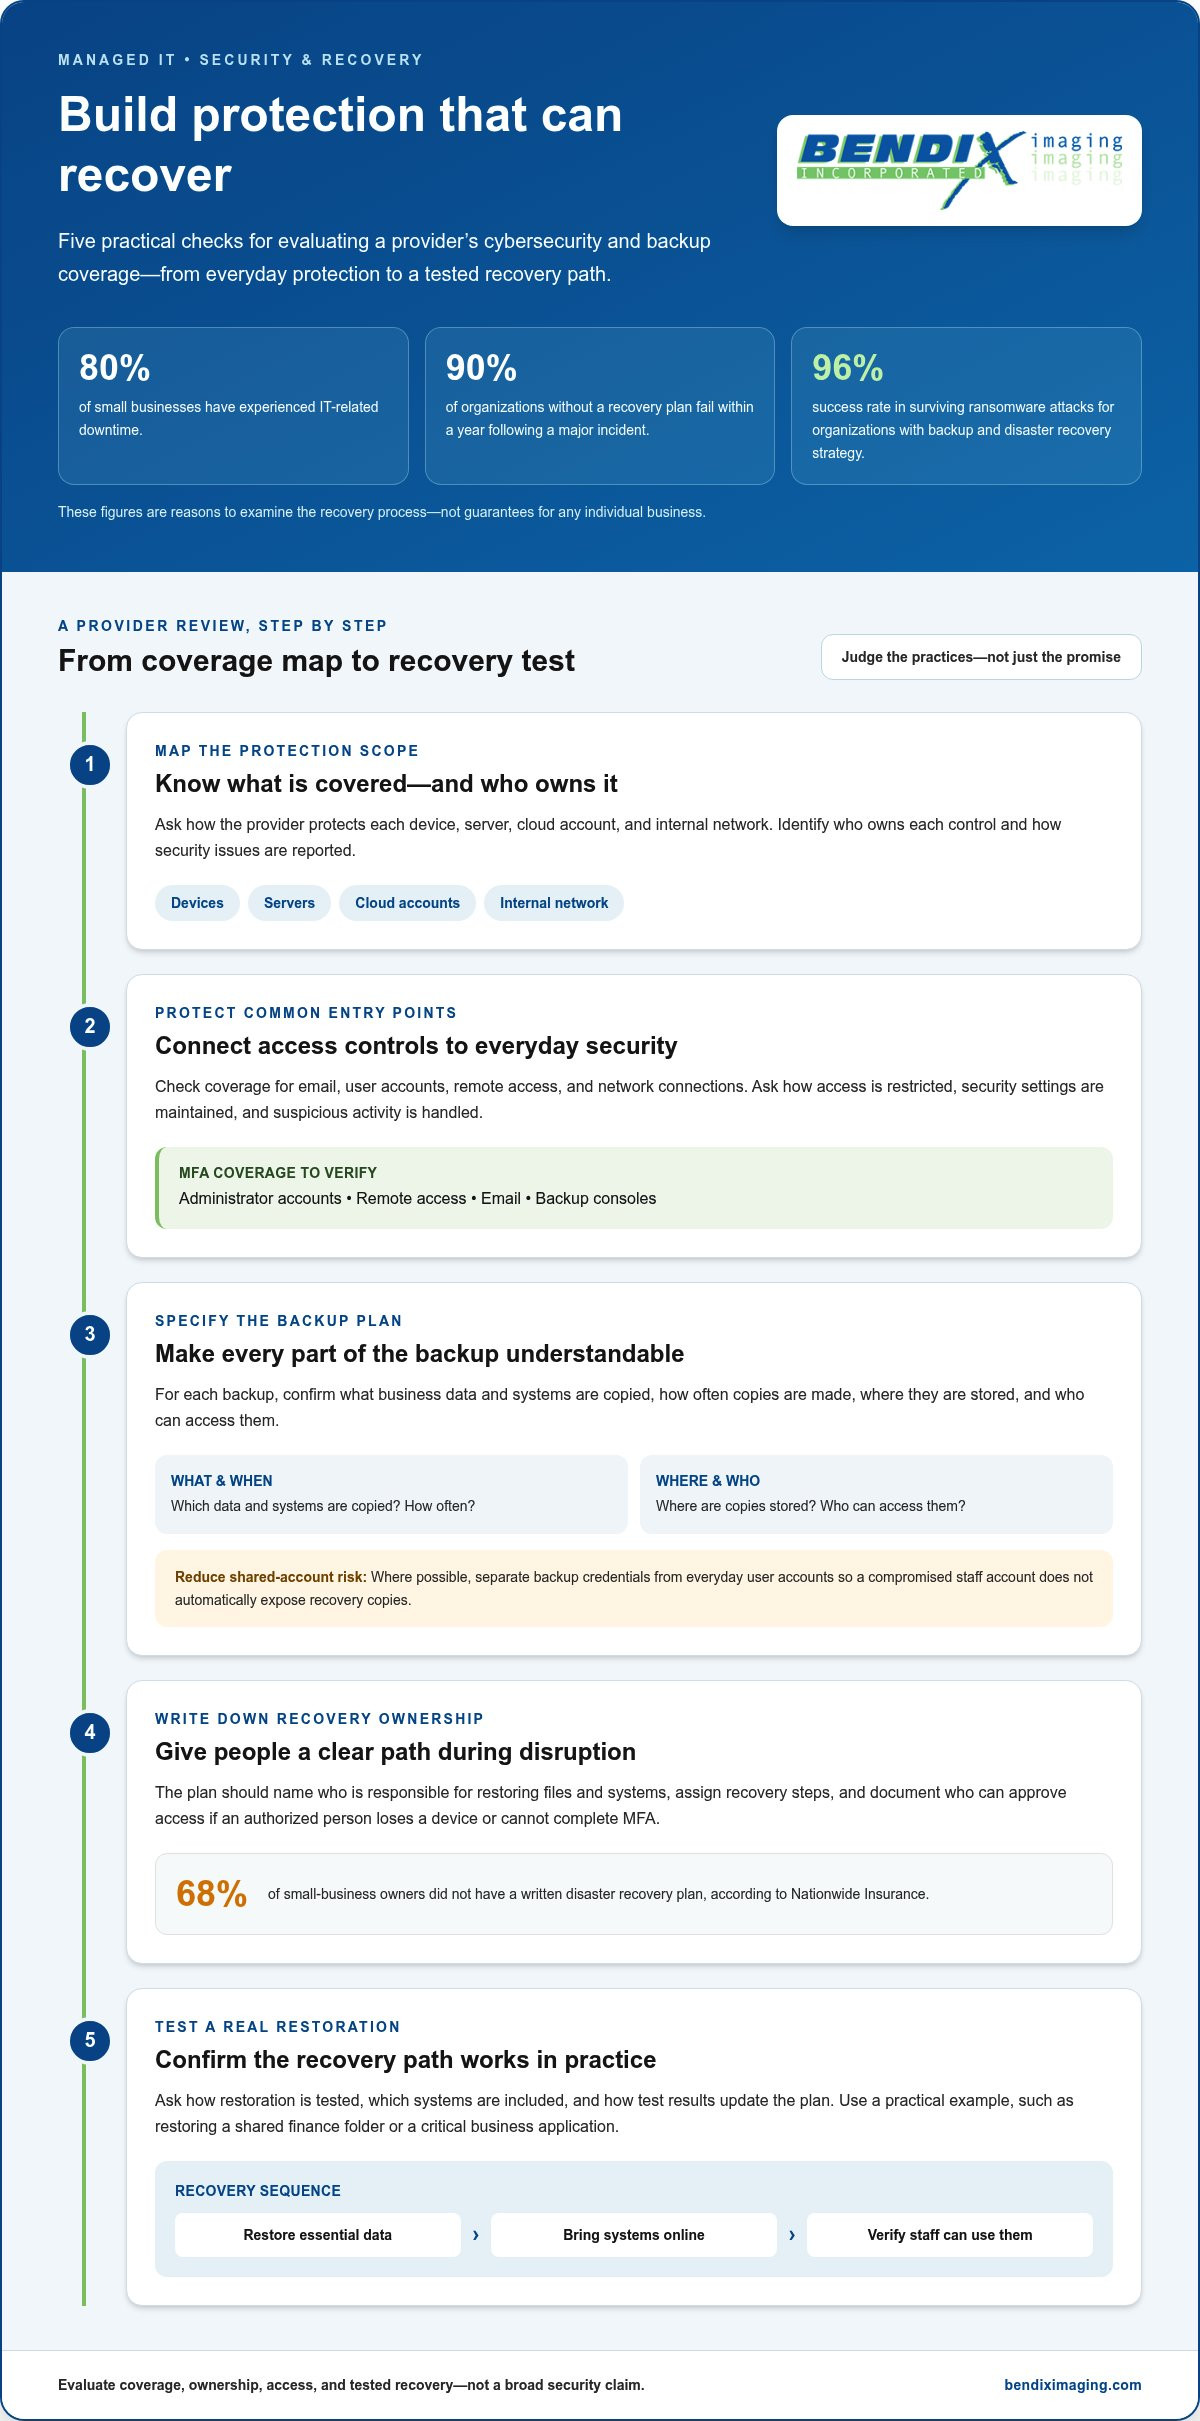
IDC research cited by the page found that 80% of small businesses had experienced IT-related downtime. A provider’s cybersecurity coverage should reduce preventable exposure and limit disruption when defenses fail. Compare specific practices, not a broad promise to keep systems secure. Ask how the provider protects each device, server, cloud account, and internal network. Then identify who owns each control and how security issues are reported.
Check whether protection covers common entry points, including email, user accounts, remote access, and network connections. A phishing email, for instance, can expose credentials, while an unprotected device can create another route into business systems. Ask how access is restricted, security settings are maintained, and suspicious activity is handled. Effective coverage connects these measures rather than treating each device as a separate problem.
Backup matters only if the business can restore usable data after an incident. Organizations without a recovery plan fail within a year following a major incident at a rate of 90%. Organizations with a backup and disaster recovery strategy have a 96% success rate in surviving ransomware attacks. Treat those figures as a reason to examine the recovery process, not as a guarantee for any one business.
Assess the backup plan step by step. Identify which business data and systems are copied, how often copies are made, where they are stored, and who can access them. Where possible, separate backup credentials from everyday user accounts. If ransomware compromises a staff account, independent access controls can help protect recovery copies. The plan should also identify who is responsible for restoring files and systems.
Recovery testing distinguishes having backup files from having a workable recovery path. Ask how restoration is tested, which systems are included, and how the results inform the plan. Use a practical example, such as restoring a shared finance folder or a critical business application. Confirm the sequence: restore essential data, bring systems back online, then verify staff can use them.
Include multifactor authentication (MFA) in the security and recovery plan. Apply it to administrator accounts, remote access, email, and backup consoles. Document who can approve access if an authorized person loses a device or cannot complete MFA. Nationwide Insurance found that 68% of small-business owners did not have a written disaster recovery plan. A written document that assigns owners, records recovery steps, and includes MFA contingencies gives internal teams a clear path to follow during disruption.
2. Security monitoring and incident response
Monitoring is useful only when alerts lead to clear action. For a mid-market business, compare providers’ monitoring scope, alert review process, and escalation path. The page recommends expecting 24/7 monitoring when evaluating a mid-market managed service provider. Confirm whether that coverage includes network devices, servers, cloud services, and security events, rather than only basic availability checks. A failed server and a suspicious login need different responses.
Network and server monitoring should help identify warning signs before staff lose access. Ask how the provider tracks device health, unusual traffic, storage capacity, and repeated service errors. Rising storage use, for example, can signal that a server needs attention before it stops accepting files. Find out who receives alerts and how issues become recorded support tickets. That link between technical signals and follow-through matters.
Response time needs careful interpretation. Many organizations expect a 15-minute response for critical outages, while a typical managed IT service response time is 1-4 hours. These figures describe different expectations, not necessarily the same service commitment. Compare how a provider defines “response”: acknowledgment, initial investigation, or active remediation. A quick acknowledgment alone doesn’t restore a business application or explain the next step.
Proactive monitoring can reduce system outages by 98%. To assess how monitoring supports prevention, examine what happens after an alert appears. A useful process assigns severity, identifies the affected systems, and records the action taken. For example, repeated login failures may prompt investigation, while a server’s rising error count may trigger maintenance. Review incident records monthly to spot recurring causes and unresolved risks.
Incident response needs a communication path that works during a disruption. Identify who reports an incident, who makes decisions, and how staff receive updates. Consider a practical scenario: an employee cannot access a shared system, but other applications still work. The response plan should identify the affected service and business impact, then give staff a clear reporting channel. This helps prevent duplicate reports and conflicting instructions.
Compare providers using the same checklist: monitoring hours, systems covered, alert priorities, response definitions, escalation contacts, and incident documentation. Then test the process with a tabletop scenario, such as a network outage during a busy workday. Note who owns each action and how progress is communicated. Reviewing alerts and incidents regularly can reveal patterns that a service description alone will not show. Look for consistent monitoring, clear ownership, and useful follow-through.
3. Compliance experience and frameworks
Over 60% of minor enterprise owners struggle to keep pace with evolving regulations. A provider’s compliance experience should therefore be assessed against your organization’s actual obligations, systems, and data practices. Start by naming the frameworks relevant to your operations, then compare the provider’s capabilities against those needs. A broad claim of “compliance support” tells you little unless it connects to specific processes, evidence, and responsibilities.
HIPAA, SOC 2, ISO 27001, CMMC, and PCI-DSS are frameworks managed service providers may support. They are not interchangeable labels. Ask the provider to explain which services relate to your selected framework and what work remains with your organization. For example, if your business is evaluating HIPAA support, discuss how access controls, data handling, incident records, and staff responsibilities fit your environment. Keep the discussion tied to your business, not a generic checklist.
Separate technical capabilities from compliance outcomes. A provider can help organize security practices, maintain relevant system records, and identify gaps, while your organization remains responsible for its decisions and obligations. Ask to see a sample report with sensitive information removed. Look for clear descriptions of the systems reviewed, findings, assigned owners, and follow-up actions. A list of technical activity is less useful if it does not explain the business impact.
Test a provider’s experience with a practical scenario. Imagine an employee needs access to a sensitive system after their role has changed. Ask how access is reviewed, who approves changes, and how the decision is documented. Then consider a service disruption: can the provider explain how incident records connect with disaster recovery planning? Specific answers show whether compliance support fits real workflows or amounts only to framework names in a presentation.
Make accountability predictable by assigning each task to a role. In your comparison notes, record who maintains system evidence, who reviews access, how findings are escalated, and when follow-up is documented. Keep these responsibilities alongside your internal procedures so staff know where provider work ends and organizational decisions begin. For example, a compliance lead could track an open finding while technical staff document the corrective work.
Assess continuity, too. Framework support should account for system changes, new tools, and evolving business processes, not just an initial review. Ask how changes are recorded and how the provider explains their effect on existing controls. Compare that process with your organization’s review cycle and disaster recovery plan. A good fit is a provider whose capabilities align with your framework priorities, produce usable reports, and support clear ownership over time.
4. Scalability and long-term partnerships
Growth changes more than headcount. New locations, applications, and business processes all place demands on your IT infrastructure. Ranked managed service providers typically serve organizations ranging from around 50 employees to several thousand. Use that range as context, not a measure of fit. Map your own likely changes, such as opening an office or adding a cloud system, then compare how each provider plans to support them.
Ask how service scope adapts as your environment changes. A business adding a location, for example, needs consistent user access, network protection, and support across sites. The provider should explain how new systems enter its management process, how responsibilities are assigned, and how changes are documented. Compare that plan with your expansion priorities. A strategic partner connects technical changes to business needs instead of treating every new device as an isolated request.
Internal IT teams may need a different relationship with a provider as the company grows. Some organizations seek outside support for defined tasks; others need broader day-to-day management. Describe your team’s responsibilities, then identify gaps such as network oversight or planning capacity. A useful partnership makes ownership clear: internal staff retain the work they lead, while the provider handles agreed responsibilities and coordinates changes with them.
Plan transitions around the complexity of your systems. MSP transitions generally take 30 to 90 days, depending on the environment’s complexity. During that period, priorities can include documenting infrastructure, organizing access, identifying dependencies, and setting support workflows. Build a transition plan that names the owner for each task and records what must be completed before service begins. That makes operational handoffs more orderly and reduces avoidable confusion.
Long-term value depends on proactive planning, not just resolving tickets. Schedule recurring reviews to discuss system changes, recurring issues, upcoming projects, and capacity needs. Before introducing a new business application, for example, review its access requirements, network impact, and support ownership. Record decisions and due dates so both teams share a view of what is changing and can keep continuity in focus as priorities shift.
Test the partnership against a realistic growth scenario. Suppose your organization adds a department and adopts a new workflow. Ask how the provider would assess the infrastructure impact, coordinate setup, and support staff afterward. Compare the answer with your internal goals and procedures. A durable fit has a defined communication path, clear ownership, and a way to adjust service scope as your organization changes. These are stronger indicators than a broad promise to scale.
5. Managed IT services and security capabilities
Managed IT combines ongoing technology support with security and maintenance. Compare the actual scope: does it cover employee accounts, business devices, network infrastructure, and routine support? An enterprise environment may need different controls and reporting from a small office, and businesses maintaining specialized hosting or hardware can look to datacenterspecialists.com for examples of how mission-critical IT environments are maintained. Match each capability to a business need, then note which tasks remain with internal staff.
Security coverage should connect network protection with everyday support. An employee who loses access to a work account needs a clear support path, while suspicious network activity needs investigation and escalation. Review service descriptions for monitoring, user support, and security ownership. Don’t assume a broad service label includes every system or task your organization relies on.
Review the agreement’s scope, service-level commitments, exclusions, renewal terms, and cancellation rules. Check how response priorities are defined, what happens when service ends, and how your data and access credentials are returned or transferred. A clear agreement names responsibilities and explains a planned exit, not just how service begins.
Local providers may offer closer coordination for regional operations, while national and international providers such as Insoft Services may support organizations across a broader geographic footprint with managed networking and cybersecurity capabilities. Compare actual service coverage, communication, and escalation arrangements rather than assuming location determines quality. Managed IT service costs depend on scope, user or device count, security needs, and compliance demands; the price depends on the case and is given after a quote request.
To assess whether reviews are genuine and current, compare dates, reviewer profiles, and specific descriptions of service experiences. Look for consistent details across independent review platforms, and note whether comments describe similar work and support conditions. Review themes worth examining include missed response expectations, unclear contract scope, weak communication, and difficult service transitions. Treat repeated, detailed concerns as signals to investigate, not automatic proof.
Leaders should also compare how the provider supports continuity during a disaster or service change. A useful example is an employee unable to access a business application: who records the issue, communicates its status, and coordinates next steps? Use this scenario to assess support ownership and operational fit. For a practical discussion of your organization’s IT support needs, connect with an IT support team.
CRN's Security 100 category recognizes MSPs with expertise in cloud-based security services. Managed IT services can achieve cost reductions of 20-30% and productivity increases of 15-25%.
BENDIX imaging: Artificial Intelligence (AI) Consulting
BENDIX imaging offers Artificial Intelligence (AI) Consulting for businesses assessing where AI could support their work. Consider this service when you need to evaluate potential uses, understand how AI fits existing operations, or weigh the technology alongside your security and IT priorities.
AI plans should account for the systems and information they depend on. BENDIX imaging also offers Managed IT Services, Cyber Security, and Network Security to address related technology and protection needs. Considering these areas together can help business leaders make informed decisions about AI adoption and the infrastructure around it.
If you’re exploring AI or reviewing your business technology needs, visit bendiximaging.com.
Make your next IT decision with confidence
Turn your comparison into a practical decision, not a stack of opinions. Use managed IT service provider reviews as one input, then define what your business needs most from a technology partner. Identify the operational concern that deserves attention first and who in your organization will own the next step. This keeps the decision tied to business priorities.
If your plans involve adopting AI, consider how that initiative fits your existing technology and security approach. BENDIX imaging offers Artificial Intelligence (AI) Consulting, Managed IT Services, and Cyber Security to support businesses working through these needs. A conversation with the team can help clarify priorities and shape a practical path forward.
Ready to discuss your business technology needs? Contact BENDIX imaging today. Take the next step with a clear view of what your organization needs, and build from there.
Frequently Asked Questions
Where can I find reviews of managed IT firms?
Start with Google Business Profiles, local business directories, and chamber of commerce or business-media rankings. Search the provider’s name alongside a nearby city, such as Watertown, Brookings, Sioux Falls, Huron, or Montevideo, to find locally relevant feedback. Read managed IT service provider reviews across multiple platforms, then compare specific details about support and service scope. Recent, experience-based comments can offer more context than a star rating alone.
What are the best-reviewed managed IT service providers in the United States?
There isn’t one universal best-reviewed provider for every organization; the right fit depends on your systems, security needs, and support expectations. The Channel Futures MSP 501 is a worldwide survey and ranking that considers growth, innovation, and operational efficiency. CRN’s Pioneer 250 recognizes MSPs focused on small and medium-sized businesses. Treat these rankings as additional context, not customer-review scores, and compare each provider’s service fit with your organization’s priorities.
Which review sites have reliable managed IT provider ratings and customer reviews?
No single review site can establish service quality on its own. Compare Google Business Profile feedback with reviews on business directories and relevant industry platforms, then look for consistent, detailed experiences across sources. Check whether comments describe the provider’s actual IT support rather than unrelated products or services. A local chamber listing or business-media ranking offers another reference point, but it does not replace direct evidence about service delivery.
What do customers praise and criticize in managed IT service provider reviews?
Look for specific comments about clear communication, helpful support, dependable follow-through, and practical guidance. Complaints worth examining may describe unresolved tickets, unclear responsibilities, recurring technical issues, or difficulty understanding service boundaries. One review is an individual account, so compare its details with other comments and the provider’s published service scope. Notice whether feedback explains what happened and how the provider responded, rather than relying only on strong praise or criticism.
How do managed IT providers compare on response times, uptime, and support quality?
Compare providers using the same definitions and service scenarios. For response, distinguish acknowledgment from active work on an issue. For uptime, clarify which systems are measured and how planned maintenance affects reporting. Assess support quality through ticket updates, resolution explanations, and follow-up on recurring problems. A sample scenario, such as a staff member losing access to a key application, helps reveal how support works beyond headline claims.
What questions should businesses ask when evaluating managed IT provider reviews?
Ask who wrote the review, when the experience occurred, and which service it describes. Does it explain the issue, communication, and outcome? Then compare those details with your requirements: which systems need support, how staff report problems, and what reporting leaders need. Ask whether the review reflects a similar business environment and service scope. This context helps you use customer feedback as evidence without treating it as a complete evaluation.
{"@context":"https://schema.org","@type":"FAQPage","mainEntity":[{"@type":"Question","name":"Where can I find reviews of managed IT firms?","acceptedAnswer":{"@type":"Answer","text":"Start with Google Business Profiles, local business directories, and chamber of commerce or business-media rankings. Search the provider’s name alongside a nearby city, such as Watertown, Brookings, Sioux Falls, Huron, or Montevideo, to find locally relevant feedback. Read managed IT service provider reviews across multiple platforms, then compare specific details about support and service scope. Recent, experience-based comments can offer more context than a star rating alone."}},{"@type":"Question","name":"What are the best-reviewed managed IT service providers in the United States?","acceptedAnswer":{"@type":"Answer","text":"There isn’t one universal best-reviewed provider for every organization; the right fit depends on your systems, security needs, and support expectations. The Channel Futures MSP 501 is a worldwide survey and ranking that considers growth, innovation, and operational efficiency. CRN’s Pioneer 250 recognizes MSPs focused on small and medium-sized businesses. Treat these rankings as additional context, not customer-review scores, and compare each provider’s service fit with your organization’s priorities."}},{"@type":"Question","name":"Which review sites have reliable managed IT provider ratings and customer reviews?","acceptedAnswer":{"@type":"Answer","text":"No single review site can establish service quality on its own. Compare Google Business Profile feedback with reviews on business directories and relevant industry platforms, then look for consistent, detailed experiences across sources. Check whether comments describe the provider’s actual IT support rather than unrelated products or services. A local chamber listing or business-media ranking offers another reference point, but it does not replace direct evidence about service delivery."}},{"@type":"Question","name":"What do customers praise and criticize in managed IT service provider reviews?","acceptedAnswer":{"@type":"Answer","text":"Look for specific comments about clear communication, helpful support, dependable follow-through, and practical guidance. Complaints worth examining may describe unresolved tickets, unclear responsibilities, recurring technical issues, or difficulty understanding service boundaries. One review is an individual account, so compare its details with other comments and the provider’s published service scope. Notice whether feedback explains what happened and how the provider responded, rather than relying only on strong praise or criticism."}},{"@type":"Question","name":"How do managed IT providers compare on response times, uptime, and support quality?","acceptedAnswer":{"@type":"Answer","text":"Compare providers using the same definitions and service scenarios. For response, distinguish acknowledgment from active work on an issue. For uptime, clarify which systems are measured and how planned maintenance affects reporting. Assess support quality through ticket updates, resolution explanations, and follow-up on recurring problems. A sample scenario, such as a staff member losing access to a key application, helps reveal how support works beyond headline claims."}},{"@type":"Question","name":"What questions should businesses ask when evaluating managed IT provider reviews?","acceptedAnswer":{"@type":"Answer","text":"Ask who wrote the review, when the experience occurred, and which service it describes. Does it explain the issue, communication, and outcome? Then compare those details with your requirements: which systems need support, how staff report problems, and what reporting leaders need. Ask whether the review reflects a similar business environment and service scope. This context helps you use customer feedback as evidence without treating it as a complete evaluation."}}]}


